Hi, I'm

Anmol Chaudhary

aka BustaYaga

Cybersecurity Analyst

I find security weaknesses in websites and networks, help fix them, and set up alerts that catch attacks early. Open to security analyst, security engineer and penetration tester roles.

Scroll ↓

I find the weak spots. And build the alerts that catch attacks.

01 / About me

I'm a cybersecurity analyst based in Dehradun, India. I test websites and company networks for weaknesses, explain what I find in clear reports, and build alerts that warn a team when something suspicious happens.

I learn by doing. I rank in the top 1% worldwide on Hack The Box, and every practice lab I solve ends up as a published writeup.

View resume
Looking for
Security Analyst, Security Engineer or Penetration Tester roles
Focus
Security testing, threat detection and network security
Based in
Dehradun, India (open to remote or hybrid)
Education
BCA, Rabindranath Tagore University (2022 - 2025)

Experience

Full-time security training & hands-on labsMay 2026 - now

Self-directed · Hack The Box · home labs

  • Rooted 20+ Hack The Box machines across web, Active Directory and network attack paths, reaching global rank #827 (top 1% worldwide).
  • A pentest-style writeup for every machine, published here once the lab retires.
Technology SpecialistJan 2026 - Apr 2026

Teleperformance

  • Supported customers live over chat and tickets in Genesys Cloud and Salesforce, keeping satisfaction above 95%.
  • Solved 98% of issues on the first contact, end to end in the Instacart CRM and admin panel.
  • Helped grow customer retention by 15% by finding the root cause of recurring problems.

02 / Skills

Skills & tools.

The areas I work in, and the tools I use to do the work.

01 / Red team

Offense

Find the way in before an attacker does.

  • 29 Hack The Box machines solved
  • 7 practice web applications tested
  • My own vulnerability scanner, Vuln-Scanner
writeups ↓

02 / Blue team

Defense

Spot the attack while it is happening.

  • A Wazuh + Suricata monitoring lab
  • Alert rules mapped to MITRE ATT&CK
  • Safe attack tests, each with a short report
detection lab ↓
01Offense

Security testing

Checking websites, apps and networks for weaknesses before attackers find them.

  • Vulnerability assessment
  • Penetration testing
  • OWASP Top 10
  • API security
  • Burp Suite
  • Metasploit
  • Nmap
  • BloodHound
02Defense

Threat detection & monitoring

Watching logs, writing alert rules and looking into suspicious activity.

  • Wazuh
  • Suricata
  • Sysmon
  • Detection rules
  • Alert triage
  • Log analysis
  • Incident reporting
  • MITRE ATT&CK
03Both sides

Networks & systems

Knowing how networks, servers and user accounts fit together, and where they break.

  • TCP/IP
  • DNS
  • IDS/IPS
  • SSH
  • Wireshark
  • Active Directory
  • Kerberos
  • Linux
04Both sides

Programming & automation

Writing small tools and scripts that cut out repetitive manual work.

  • Python
  • Bash
  • SQL
  • Flask
  • REST APIs
  • Docker
  • Git
  • GitHub Actions
05Both sides

Communication

Turning technical findings into clear reports that anyone on a team can act on.

  • Report writing
  • Root cause analysis
  • Explaining issues simply
  • Customer support

Featured projects

03.01 / Featured project · Vulnerability assessment & penetration testing

End-to-end security testing: map what is exposed, find the weak spots in web apps and company networks, prove they are real in a safe lab, and write a report on how to fix each one.
VAPTView

Full VAPT web · network · tooling

  • Tested 7 practice web applications and several practice company networks
  • Built my own scanner (Vuln-Scanner) to speed up the first checks
  • Every finding ends in a clear report with a fix, then a re-test
  • Burp Suite
  • Nmap
  • BloodHound
  • Wireshark
  • Python

03.02 / Featured project · Threat detection & monitoring

A small security operations setup built from free tools: Wazuh collects logs from Linux and Windows machines, Suricata watches network traffic, and alerts fire when an attack is spotted.

DETECTIONView

Wazuh + Suricata Security Monitoring Lab home lab · 2026

  • Logs from servers, a Windows PC and network traffic in one place
  • Custom alert rules, each linked to a known attack technique (MITRE ATT&CK)
  • Safe attack tests, automatic blocking, and a short report for every test
  • Wazuh
  • Suricata
  • Sysmon
  • MITRE ATT&CK

04 / Writeups

Practice, written up.

Hack The Box is a legal training platform with practice systems that are built to be hacked. For every one I solve, I publish a short writeup: what was wrong, how I found it, and how it should be fixed.

See all writeups ↓

05 / All writeups

All writeups

Every Hack The Box lab I have solved: my newest writeup on top, then the open ones, then the locked ones. Click one to read it. Writeups on labs that are still active are encrypted and open with a passphrase, which I share on request.

Hack The Box · Highest tier · Season 12 Platinum #827 global ranking
5 open · 14 locked
Hack The Box labs I have solved, with the state of each writeup
MachineSystemDifficultySolvedWriteup
BedsideLatest Linux Medium Passphrase
Checkpoint Windows Easy Read writeup
CCTV Linux Easy Read writeup
Reactor Linux Easy Read writeup
DevHub Linux Medium Read writeup
Facts Linux Easy Read writeup
Unclaimed Windows Medium Passphrase
Enigma Linux Easy Passphrase
Paperwork Linux Easy Passphrase
Management Linux Easy Passphrase
Cohort Linux Easy Passphrase
Takeoff Linux Hard Passphrase
DutyBound Linux Medium Passphrase
Stream Linux Medium Passphrase
Touch Windows Easy Passphrase
Layover Linux Medium Passphrase
Nimbus Linux Hard Passphrase
Kobold Linux Easy Passphrase
Connected Linux Easy Passphrase
Cap – Easy – Not written yet
Silentium – Easy – Not written yet
Conversor – Easy – Not written yet
Expressway – Easy – Not written yet
Soulmate – Easy – Not written yet
CodePartTwo – Easy – Not written yet
Editor – Easy – Not written yet
Outbound – Easy – Not written yet
Artificial – Easy – Not written yet
Voleur – Medium – Not written yet

I've also solved 10 other labs that I haven't written up yet.

06 / Achievements

Certified.Ranked.

Hack The Box · Global Top 1% worldwide
Hack The Box writeups published
  • 5 open to read
  • 14 locked while the lab is active
  • Easy to Hard, Linux and Windows
19 writeups published
Built and shipped projects
  • 5 security projects, 2 others
  • 4 with public source code
  • Testing, detection and tooling
7 projects
Earned certifications
  • OpSec · Just Hacking Training
  • Google Cybersecurity · Google
  • 2 in progress: CompTIA Security+, HTB Junior Cybersecurity Associate
  • Plus a BCA degree, 2022–2025
2 certifications

Certifications & education

02 / Professional certificateEarned Google Cybersecurity Professional Certificate October 2024 · ID 30e489e1 Google2024
03 / DegreeEarned Bachelor of Computer Applications (BCA) 2022 - 2025 Rabindranath Tagore University2022–25
04 / CertificationIn progress CompTIA Security+ CompTIANow
05 / CertificationIn progress HTB Certified Junior Cybersecurity Associate (CJCA) Hack The BoxNow

Highlights

[LEAD]

Founded and ran a 500+ member online community

Built the platform myself (about 60,000 lines of code) and ran support, moderation and releases for real users.

[REPORTS]

5 public writeups

Each one explains, in plain steps, what was wrong, how I found it and how to fix it.

[TOOLS]

Built my own security tooling

Vuln-Scanner checks a computer for known security issues; its source code is public on GitHub.

[SUPPORT]

Customer-facing problem solving

Explained technical issues to non-technical customers every day at Teleperformance.

07 / Resume

The one-page version.

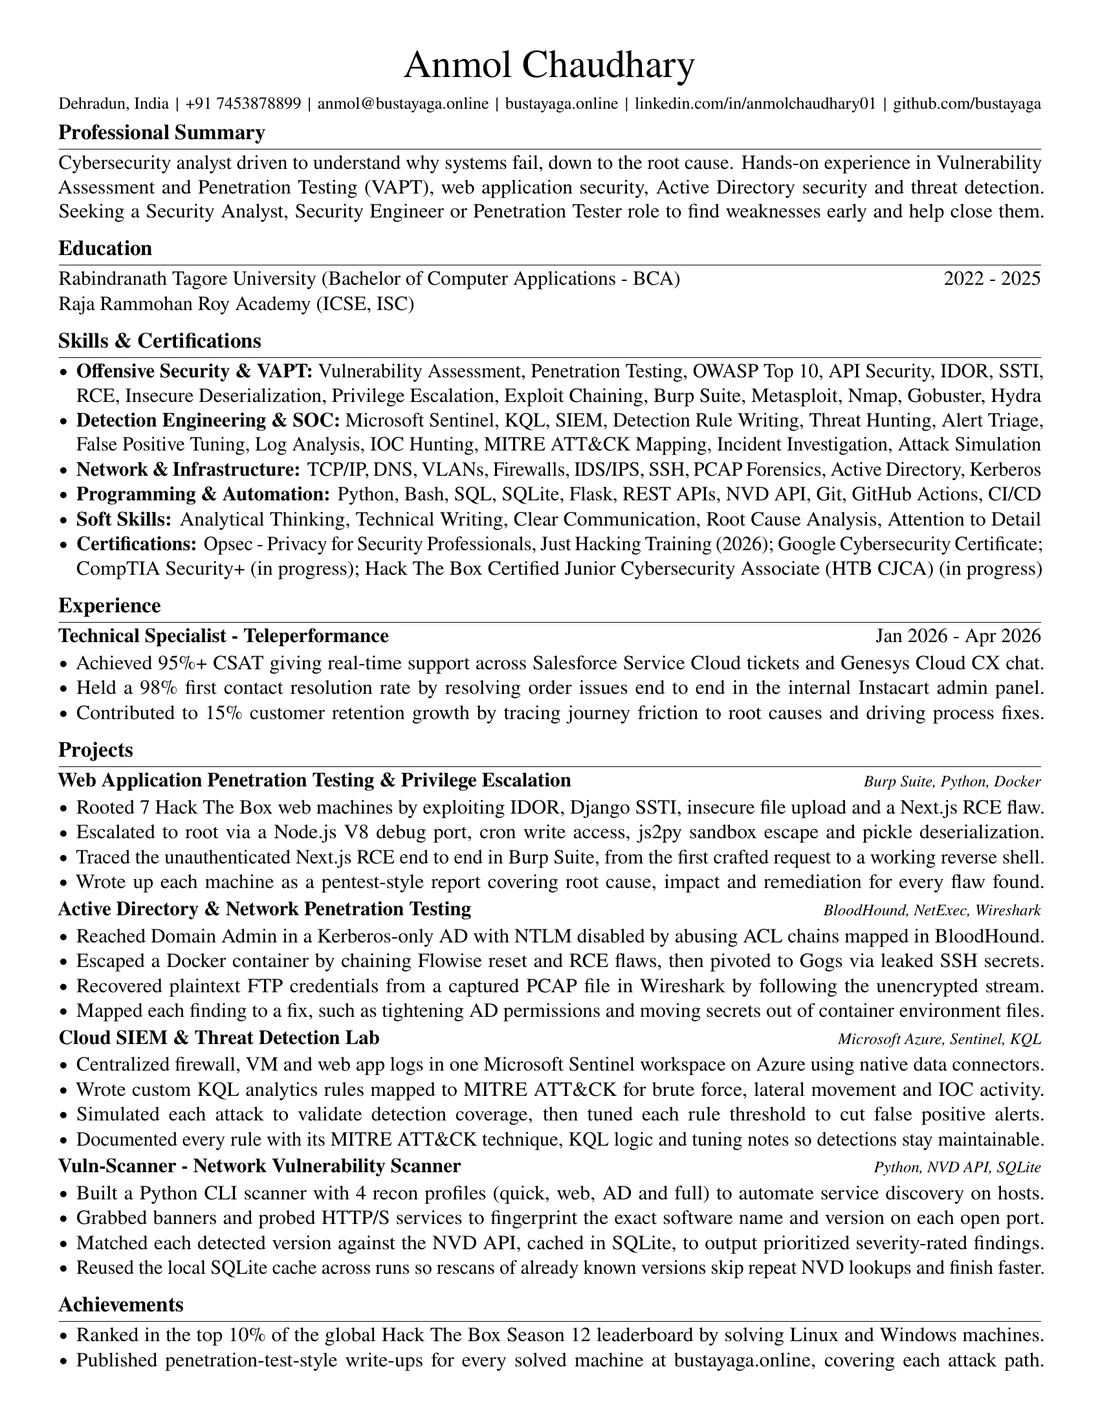
Preview of Anmol Chaudhary's one-page cybersecurity resume

Cybersecurity Resume

  • Summary ✓
  • Skills ✓
  • Certifications ✓
  • Experience ✓
  • Projects ✓

Everything on one page: security testing, threat detection and networking, 20+ Hack The Box machines, four projects, and customer-facing technical support at Teleperformance.

08 / Contact

Let's talk.

Open to security analyst, security engineer and penetration tester roles. The quickest way to reach me is email.

[email protected]

Dehradun, India · Remote / Hybrid · © 2026 Anmol Chaudhary · Privacy & terms · Updated November 2026